Why Are Your Mobile Apps Becoming Harder to Secure? Modern Security Challenges
Understanding Modern Mobile Security Challenges

Introduction
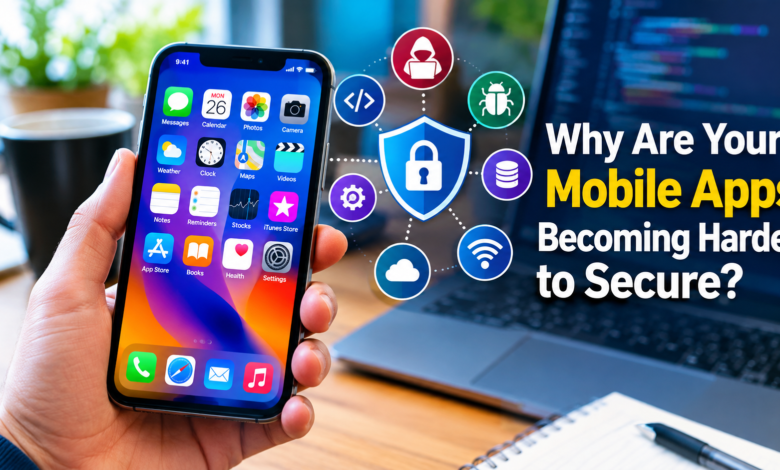
Mobile applications have become more powerful, connected, and dependent on external technologies. Apps now communicate with cloud services, APIs, payment systems, analytics platforms, third-party SDKs, authentication providers, and many other components. This expanding ecosystem has also made security more complicated.
The challenge is no longer limited to protecting the application code itself. Developers must consider device storage, authentication, network communication, permissions, APIs, third-party dependencies, privacy, build systems, and the underlying mobile platform.
The OWASP Mobile Application Security Verification Standard (MASVS) currently organizes mobile security around areas including storage, cryptography, authentication, networking, platform interaction, code, resilience, and privacy.
The Mobile Attack Surface Is Expanding
One major reason mobile apps are becoming harder to secure is the growth of their attack surface.
A modern application may contain the company’s own code alongside open-source libraries, commercial SDKs, frameworks, analytics tools, advertising components, authentication services, and cloud APIs.
Each additional component can introduce another security dependency.
OWASP specifically identifies third-party components and dependencies as an important mobile-security concern. Vulnerable libraries can expose applications to data compromise, unauthorized code execution, and other security problems.
This means developers increasingly need to understand not only what they wrote, but also what their application includes.
Third-Party SDKs Create New Security Challenges
Third-party SDKs can save development time, but they also increase the amount of code and functionality that an application depends on.
An SDK may collect information, communicate with external servers, access device capabilities, or introduce additional dependencies. If its security or privacy practices are inadequate, the application can inherit some of those risks.
OWASP’s privacy guidance emphasizes minimizing access to sensitive data and considering how third-party SDKs handle information and user consent.
For development teams, this makes dependency management an ongoing security responsibility rather than a one-time task.
Supply-Chain Risks Are Becoming More Important
The software supply chain is another reason mobile security has become more difficult.
Applications are assembled from numerous components. A compromised library, SDK, build tool, or development dependency can potentially introduce unwanted functionality into an otherwise legitimate application.
OWASP’s 2026 MASWE release specifically added a weakness covering malicious code included in an application, including code introduced through compromised dependencies, SDKs, build tools, or other supply-chain attacks.
This highlights an important change in modern security thinking: developers must protect the entire software-production process, not simply inspect the finished source code.
APIs Connect Mobile Apps to Larger Systems
A mobile application is rarely an isolated product.
Most modern apps communicate with backend APIs that handle accounts, databases, payments, profiles, content, or other services. Consequently, mobile security depends heavily on the security of those connections.
OWASP recommends designing secure APIs, using appropriate authentication mechanisms, protecting tokens, and regularly reviewing credentials and access controls.
A secure-looking mobile interface therefore does not automatically mean the entire application ecosystem is secure.
Sensitive Data Is Difficult to Protect
Mobile apps frequently process personal information, authentication credentials, session information, financial information, location data, and other sensitive content.
Some of this information may need to be stored locally. OWASP’s MASVS requires sensitive data to be securely stored and identifies problems such as unencrypted sensitive information and improperly protected cryptographic keys as mobile weaknesses.
Developers therefore need to determine:
- What information does the app actually need?
- Where is it stored?
- Who can access it?
- How long should it remain available?
- Is it encrypted appropriately?
- Could another component access it unnecessarily?
Reducing unnecessary data collection can reduce the consequences of a security incident.
Mobile Platforms Keep Changing
Android and iOS continue to evolve, introducing new APIs, permissions, privacy controls, security mechanisms, and platform restrictions.
That creates a moving target for development teams.
Security practices that were acceptable several years ago may become outdated as operating systems change. OWASP’s mobile guidance therefore includes secure interaction with the underlying platform as a distinct security area.
Developers must continually review platform APIs and replace deprecated or inappropriate functionality.
Authentication and Authorization Are More Complex
Authentication determines who a user is, while authorization determines what that user is allowed to do.
Modern applications often involve multiple authentication methods, devices, sessions, APIs, and backend services. A mistake in one part of this system can create unexpected access paths.
OWASP’s current mobile security model treats authentication and authorization as a dedicated control area, reflecting their importance in protecting application functionality and user information.
Security teams therefore need to test access control throughout the application rather than assuming that a successful login automatically means the system is secure.
Untrusted Input Remains a Major Problem
Mobile applications receive data from many sources, including users, networks, files, other applications, and platform components.
That information should not automatically be trusted.
OWASP’s MASVS-CODE-4 requires applications to validate and sanitize untrusted inputs because improperly handled input can contribute to problems such as injection attacks, insecure deserialization, and unsafe data processing.
This becomes especially important when mobile applications interact with WebViews, deep links, external files, or backend services.
Privacy Is Now Part of Application Security
Security and privacy are closely connected.
An application may be technically functional while still collecting more information than necessary. Excessive permissions, unnecessary tracking, or poorly controlled third-party data sharing can increase privacy risks.
OWASP’s MASVS includes privacy as one of its dedicated control groups and emphasizes minimizing access to sensitive data and resources.
Developers should therefore consider privacy requirements during architecture and design rather than adding privacy controls after development is complete.
Security Testing Is Becoming More Structured
As mobile applications become more complicated, testing also needs to become more systematic.
OWASP’s Mobile Application Security Testing Guide works alongside MASVS, while the newer Mobile Application Security Weakness Enumeration provides a structured way to describe specific weaknesses. In August 2026, OWASP announced MASWE version 1.0.0 with 78 fully documented weaknesses.
The relationship can be understood as:
Security requirements → weaknesses → security tests → practical demonstrations
This structure helps development and security teams connect high-level requirements with concrete testing activities.
How Developers Can Make Mobile Apps Easier to Secure
Security does not have to become an obstacle to development. The key is integrating it throughout the development lifecycle.
Start With Secure Architecture
Security should be considered during application design rather than treated as a final testing phase. OWASP recommends secure-by-design principles such as least privilege, defense in depth, and separation of concerns.
Control Dependencies
Maintain an inventory of libraries and SDKs. Monitor them for known vulnerabilities, remove unnecessary components, and update dependencies responsibly. OWASP also recommends using an SBOM to improve visibility into application components.
Minimize Sensitive Data
Only collect information that the application genuinely needs. Limit permissions and carefully evaluate how data moves between the app, backend services, and third-party components.
Test APIs and Application Logic
Security testing should cover authentication, authorization, input validation, API communication, storage, and platform interactions rather than focusing only on the visible mobile interface.
Keep Security Requirements Updated
Mobile security changes as platforms, frameworks, dependencies, and threats change. Regular reviews help prevent old assumptions from becoming security weaknesses.
Conclusion
Mobile apps are becoming harder to secure because they are no longer simple standalone programs. They are complex ecosystems connecting devices, users, APIs, cloud services, third-party SDKs, open-source libraries, operating systems, and software supply chains.
The solution is not simply adding more security checks at the end of development. Security needs to be considered throughout architecture, coding, dependency management, testing, deployment, privacy design, and maintenance.
Current OWASP guidance reflects this broader approach, with dedicated controls for storage, cryptography, authentication, networking, platform interaction, code, resilience, and privacy. Its 2026 MASWE 1.0 release further demonstrates how mobile-security weaknesses are being organized into a more structured framework.
For development teams, the central lesson is straightforward: the more connected and feature-rich a mobile application becomes, the more important continuous, systematic security practices become.